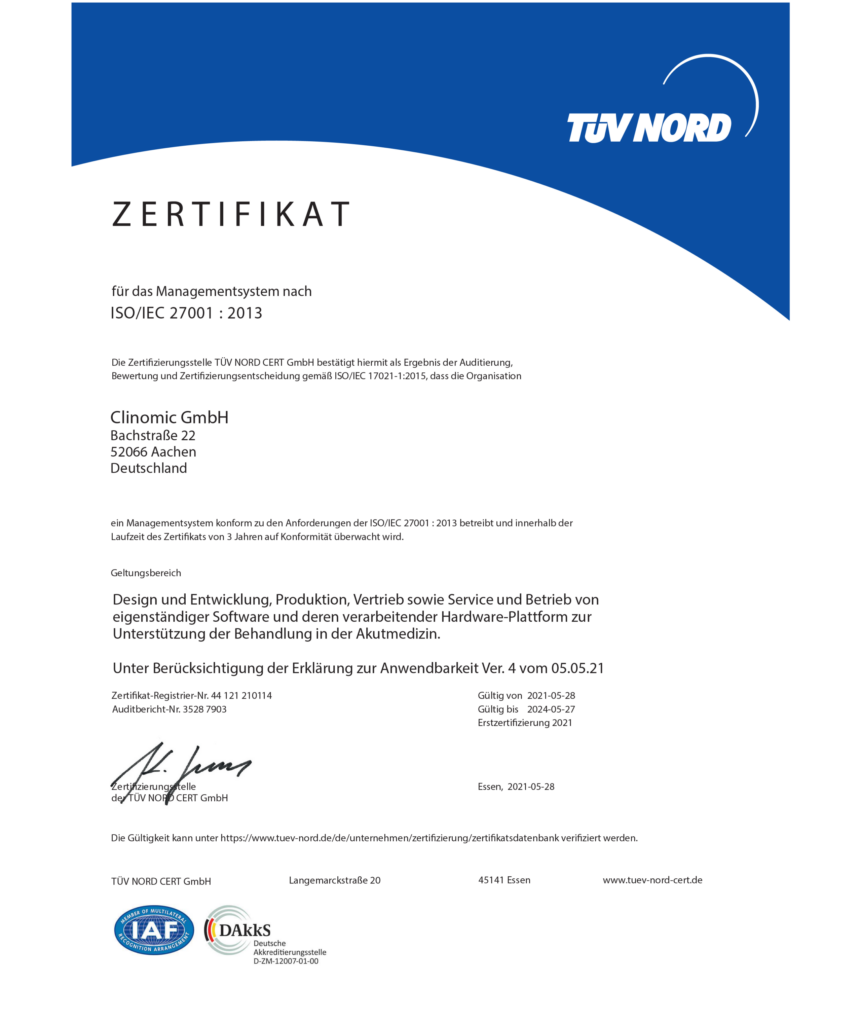
Clinomic received the ISO/IEC 27001 certificate
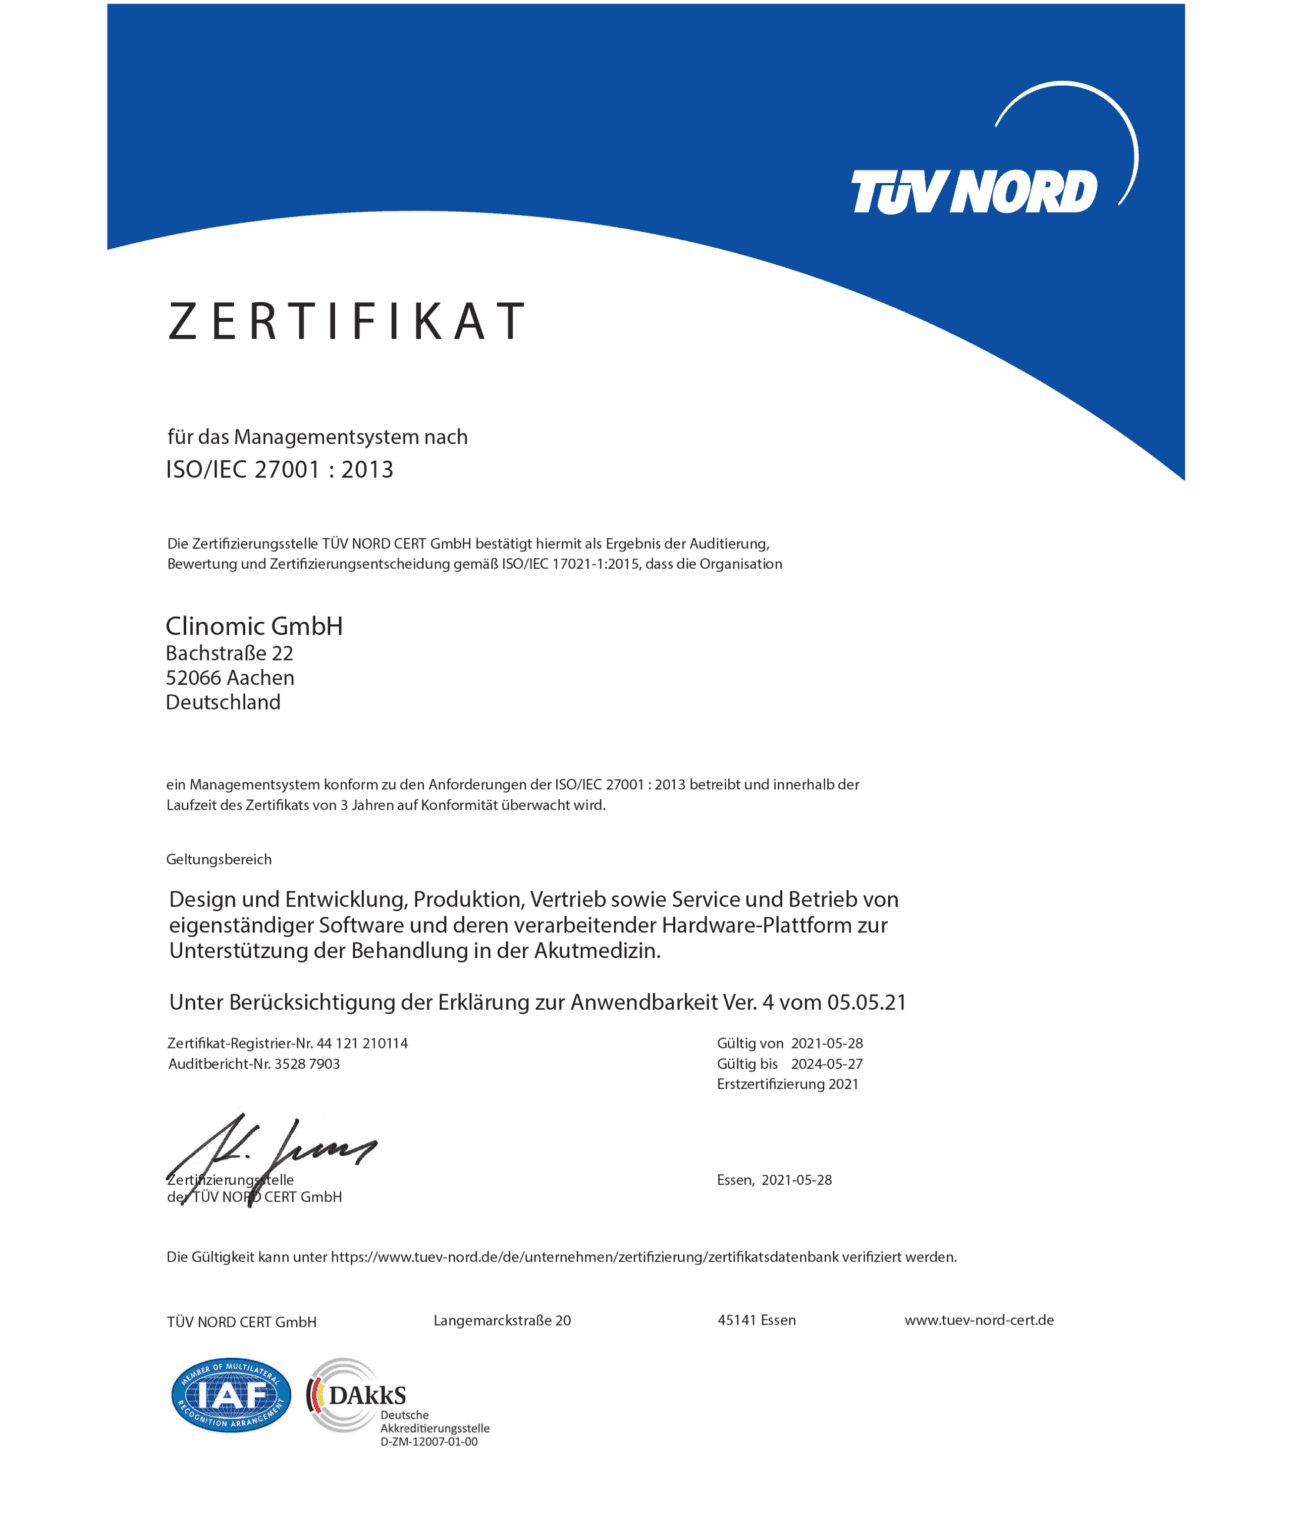
Last month, we received the ISO/IEC 27001:2013 certificate by TÜV Nord IT!
ISO/IEC 27001:2013 is an international standard that guides organizations to apply sufficient security measures of information. It details requirements for establishing, implementing, maintaining, and continually improving an information security management system (ISMS).
Our Information Security Management System (ISMS) ensures a clear and structured approach in securing the information related to our business processes. The ISMS resulted in establishing a management system that contains controls which are added to our security measures. The criteria of those controls highly depend on three important factors: confidentiality, integrity, and availability (CIA). Those factors affect the information of any organization. Clinomic analyzed the stakeholders’ requirements and established the CIA factors as an objective for the ISMS.
Both the QM department and the IT department are continuously applying, analyzing, and improving the controls used to secure the information. Therefore, threats and vulnerabilities which affect the CIA factors are continuously analyzed and monitored by adapting to the Business Continuity Management established by the ISMS. We are thankful for the contribution of everyone at Clinomic, in particular the Quality Management!