Security and certification
Certified as a medical device, audited for information security.
monaOS is a Class IIa medical device under the EU MDR. Clinomic's quality management is certified to ISO 13485 by TÜV SÜD, its information security to ISO/IEC 27001 by TÜV NORD CERT, and the Clinomic Cloud Services hold a BSI C5 Type 2 attestation for June 2025 to May 2026 (basic criteria), audited by IT AUDIT GmbH.
Certified
Certified and attested, with every document to download
EU MDR, Class IIa
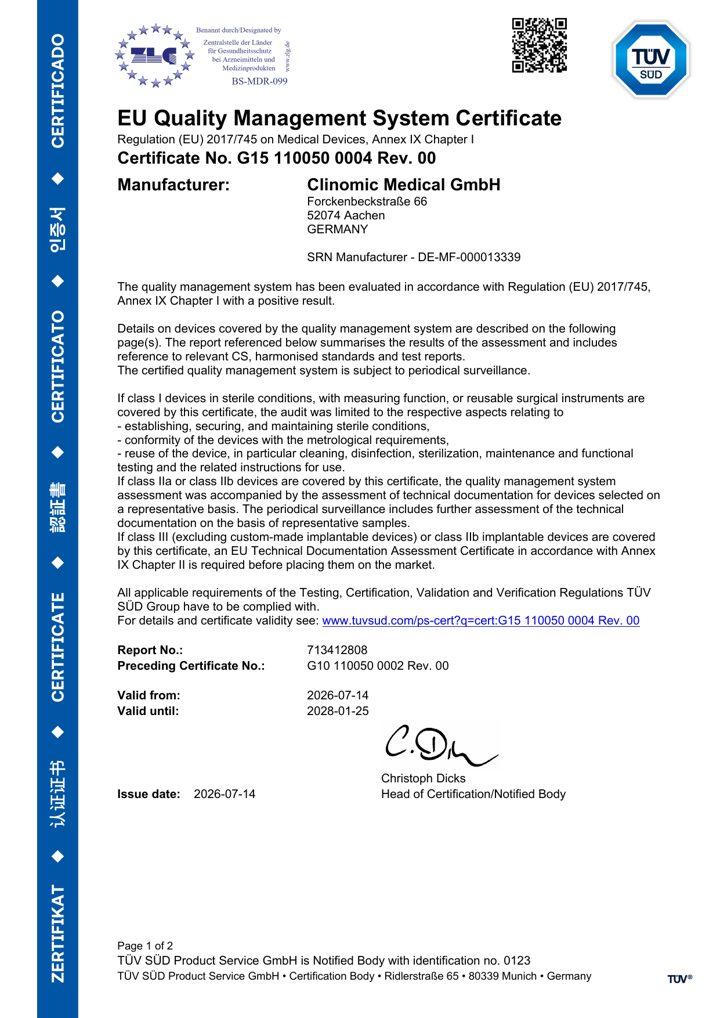
EU quality management system certificate under the Medical Device Regulation, Annex IX, for software as a Class IIa medical device.
- Issued by
- TÜV SÜD Product Service, notified body 0123
- Holder
- Clinomic Medical GmbH
- Valid
- Until 25 January 2028
ISO 13485
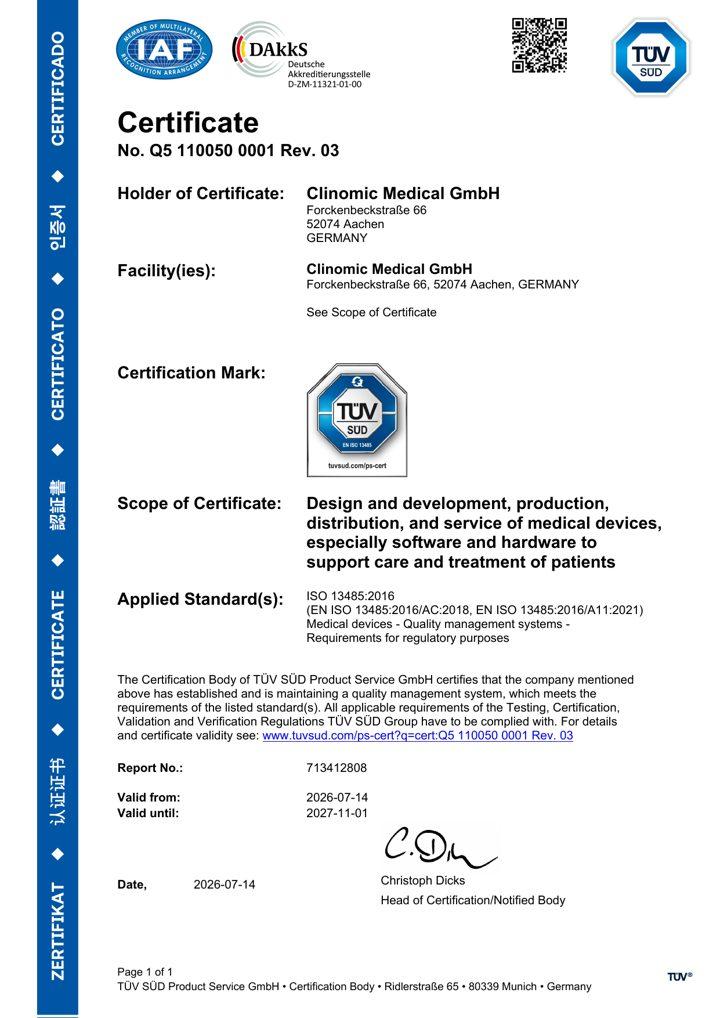
Quality management for the design, development, production, distribution and service of medical devices.
- Issued by
- TÜV SÜD Product Service
- Holder
- Clinomic Medical GmbH
- Valid
- Until 1 November 2027
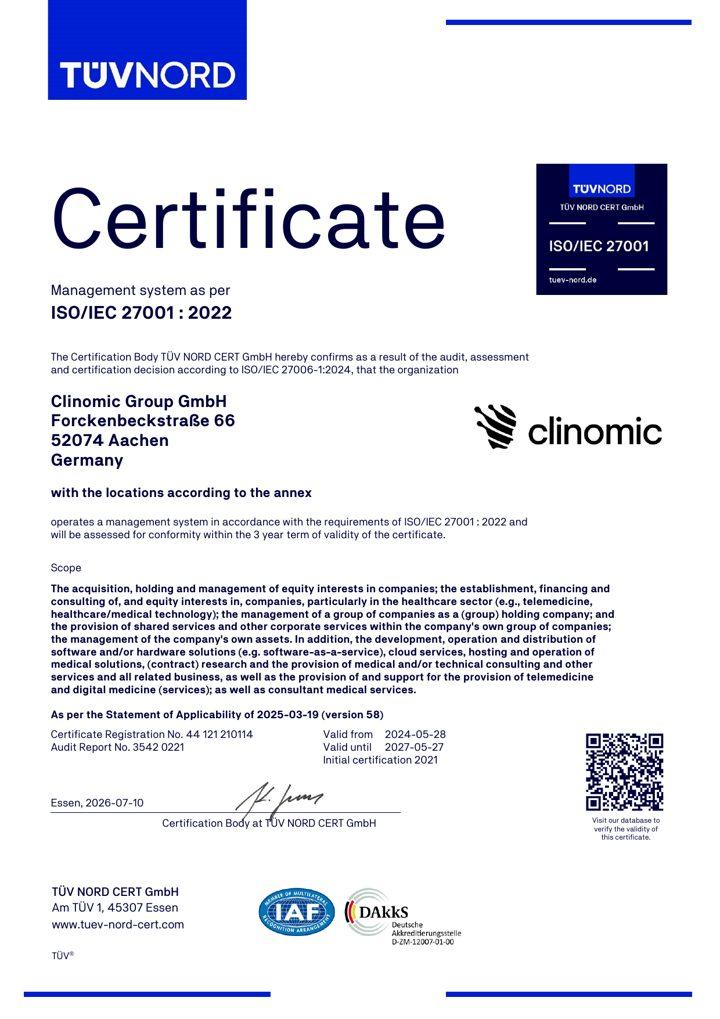
ISO/IEC 27001
Information security management for the group, including software as a service, cloud services and the hosting and operation of medical solutions.
- Issued by
- TÜV NORD CERT
- Holder
- Clinomic Group GmbH, with the locations in the annex
- Valid
- Until 27 May 2027
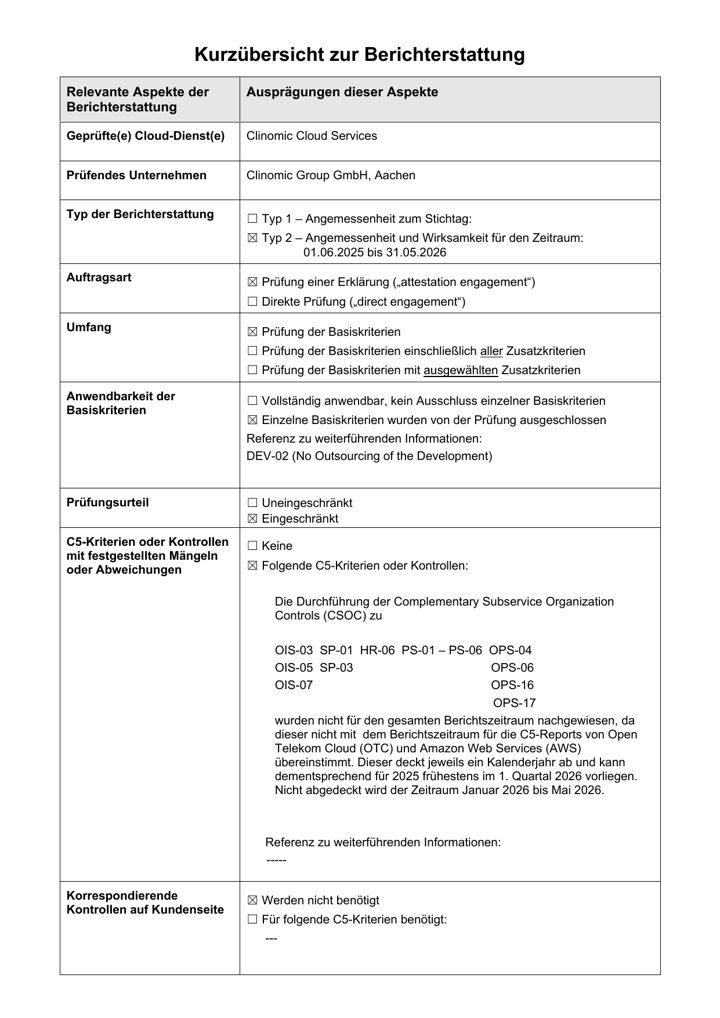
BSI C5 Type 2
Type 2 attestation against the German federal cloud security catalogue (BSI C5) for the Clinomic Cloud Services.
- Service
- Clinomic Cloud Services
- Period
- June 2025 to May 2026, basic criteria
- Auditor
- IT AUDIT GmbH
- Report
- Summary, in German
In the product
Every entry has an author, every change a history
Personal sign-in
Hospital credentials or a badge at the bedside terminal, and the session locks after inactivity.
A second sign-in where it matters
Restricted clinical operations ask for re-authentication before they go through.
Roles that match the ward
Physician, nurse, administrator. Changes entered by nursing wait for a physician's confirmation.
Every change on record
Each save carries the practitioner's name, with the field's value before and after.
Multi-tenant, one tenant per hospital
Each hospital's data is separated in the data layer and in access control, and reaches its own tenant over one encrypted, defined connection.
Research on de-identified data
A de-identification stage sits between the record and every secondary use.
FAQ
Questions security officers ask first
Who can see patient data?
Users who have signed in personally, within their role. Roles are configured per hospital during deployment and every access is attributable.
What is recorded when a value changes?
The audit trail records the field, its value before and after, the time and the practitioner's full name. Earlier values are kept, and entries marked as entered in error stay in the audit trail.
Can we verify the certificates?
Yes. Each certificate names its certification body and registration number; TÜV SÜD and TÜV NORD CERT publish validity checks online, and the PDFs are linked on this page and under Instructions for use.
Bring your security questionnaire
We answer it with the people who built and operate the platform, and walk your team through the controls on a live installation.